Tags
A software build can pass technical QA and still fail the people who use it. User acceptance testing, or UAT, gives business representatives a controlled way to prove that critical work can be completed before launch, final acceptance, or payment. The evidence should support a decision, not merely fill a spreadsheet.
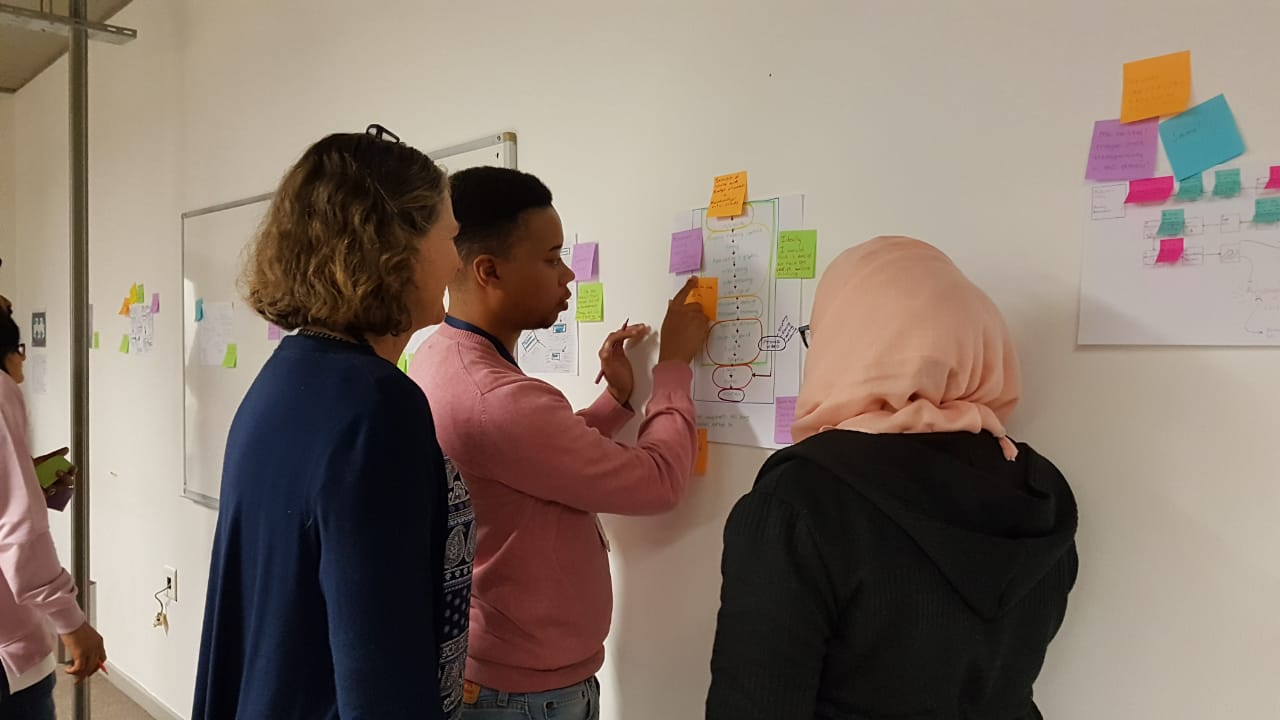
Cross-functional acceptance work depends on business stakeholders reviewing release evidence together. Photo: Bea y Fredi, CC BY 2.0, via Wikimedia Commons.
A user acceptance testing checklist is a business-led plan for proving that software supports real workflows before release. It defines readiness, representative users, scenarios, data, expected results, defect handling, exit criteria, evidence, and sign-off authority so acceptance becomes a defensible go-live decision.
UAT asks whether the delivered system is fit for its agreed business purpose. The checklist should connect every important journey to a requirement, named tester, expected outcome, observed result, issue decision, and approval. It belongs near the end of delivery, but the acceptance model should be designed while scope is still negotiable.
LeWebsite’s custom software development service connects requirements, implementation, integrations, testing, and launch controls. A useful UAT package lets a buyer verify the promised operating result instead of accepting a system because its screens load or a development team says the sprint is complete.
Quality assurance verifies whether software behaves correctly against technical specifications, while UAT verifies whether business users can complete agreed work with acceptable risk. QA usually finds defects in functions and integrations; UAT confirms workflows, decisions, permissions, outputs, and outcomes before the business accepts release.
| Control | Primary question | Typical owner | Evidence |
|---|---|---|---|
| Unit testing | Does an individual component behave as coded? | Developer | Automated test result |
| Integration testing | Do connected systems exchange and handle data correctly? | Engineering or QA | Interface and failure-path results |
| System QA | Does the complete build meet functional and nonfunctional specifications? | QA team | Test suite, defect log, regression result |
| Security verification | Do security controls meet the selected requirements? | Security and engineering | Verification record and unresolved risks |
| User acceptance testing | Can authorized users complete critical business journeys acceptably? | Business owner and representative users | Scenario results, exceptions, and sign-off |
UAT should consume prior QA evidence, not repeat every technical test manually. The NIST Secure Software Development Framework treats verification, review, vulnerability handling, release integrity, and retained evidence as development responsibilities. Business acceptance sits above those controls; it does not replace them.
The team that built the feature can explain it, repair defects, and support testing, but should not be the only group deciding whether business needs were met. Independent business representatives must perform or witness critical scenarios and retain authority to reject, conditionally accept, or approve the release.
Technical tests often isolate components. Business users should follow end-to-end work: receive a lead, verify identity, create a quote, obtain approval, collect payment, trigger fulfillment, update the CRM, and confirm reporting. A journey can fail even when every individual API and screen passes separately.
Start UAT only when scope is stable, system and integration testing are sufficiently complete, the candidate build is identified, environments and test data are ready, critical requirements are traceable, testers are trained, defects have owners, and entry, exit, and sign-off rules are approved.
A rushed UAT cycle often begins with a moving build, missing accounts, broken integrations, incomplete data, or undefined expectations. Business testers then spend limited time diagnosing setup failures instead of validating outcomes. Record every entry criterion with an owner and evidence; do not mark “ready” because a meeting date arrived.
Record the release identifier, deployment timestamp, enabled feature flags, configuration version, integration endpoints, database snapshot, and known limitations. If the build changes, identify affected scenarios and rerun them. Silent changes during UAT make results impossible to interpret and can invalidate previously recorded approval.
Test data should represent real volumes, roles, edge cases, formats, relationships, and failure conditions while protecting personal or confidential information. Use synthetic or masked data where appropriate. Document who created it, what scenarios it covers, how it is secured, and when it will be removed.
A named business sponsor owns acceptance risk, a UAT lead manages the process, and representative users execute critical scenarios. Product, operations, finance, security, support, and compliance specialists review relevant outcomes. Developers and QA support diagnosis, but business authority decides whether remaining risk is acceptable.
| Role | Responsibility | Cannot be left ambiguous |
|---|---|---|
| Business sponsor | Owns outcome, risk tolerance, and final decision | Who can approve, conditionally approve, or stop release |
| UAT lead | Plans scope, schedule, evidence, triage, and reporting | Who controls the official result set |
| Representative users | Execute real workflows using appropriate roles | Which user groups and exceptions are covered |
| Product or business analyst | Maintains requirements and traceability | Which source requirement defines success |
| QA and engineering | Prepare build, support defects, and run regressions | Who fixes, retests, and communicates changes |
| Security, privacy, or compliance owner | Reviews applicable specialist controls | Which risks require separate approval |
The selected testers must understand the work, not merely the interface. Include people who perform high-volume tasks, approve exceptions, use assistive technology, reconcile money, handle customer data, and support failures. One product manager clicking the happy path cannot represent every role, permission boundary, or operational consequence.
Convert each critical requirement into a realistic business scenario with a starting state, user role, data, steps, expected outcome, evidence, and pass rule. Link scenarios to requirements and risks, then include happy paths, permitted alternatives, validation failures, permission boundaries, integrations, and recovery behavior.
Start with the approved requirements document, user stories, process maps, and software statement of work. If acceptance criteria remain vague, resolve them before testing. “Works correctly” and “easy to use” are not repeatable results; specify the observable state, timing, calculation, message, permission, output, or handoff.
Give first priority to revenue, payment, identity, privacy, authorization, inventory, scheduling, customer communication, regulatory, data-integrity, and irreversible workflows. A cosmetic defect and an incorrect invoice may both fail a test, but they should not receive the same release consequence or escalation path.
Assign identifiers to requirements, scenarios, test cases, defects, fixes, and retests. A simple traceability matrix should show whether every critical requirement has evidence and whether every failed result reached a documented disposition. This prevents attractive low-risk scenarios from hiding uncovered high-risk obligations.
Every UAT case should record an identifier, linked requirement, business objective, tester and role, build, environment, preconditions, data, steps, expected result, actual result, evidence, pass status, defect reference, severity, retest result, and approval. Missing context makes failures difficult to reproduce or defend.
| Field | Purpose | Example |
|---|---|---|
| Scenario and requirement ID | Preserves traceability | UAT-ORD-014 / REQ-112 |
| Role and preconditions | Defines permission and starting state | Regional manager; approved customer and active price list |
| Test data | Makes the result repeatable | Customer, product, tax region, currency, and discount values |
| Expected result | Defines pass before execution | Order total, approval status, notification, and CRM update |
| Actual result and evidence | Shows what happened | Timestamp, screenshot, record ID, log, and report output |
| Disposition | Connects failure to a release decision | Fix, retest, defer with owner, accept risk, or block |
Evidence should prove the outcome without exposing unnecessary customer data or secrets. Prefer controlled screenshots, generated record identifiers, report exports, timestamps, and test logs. Never place credentials, access tokens, or unrestricted production data in the UAT workbook or defect system.
Test beyond the central screen by validating every critical integration, role, permission boundary, notification, report, import, export, failure path, accessibility need, and recovery step. Use realistic edge cases such as duplicates, missing fields, time zones, currencies, large records, interrupted connections, retries, and unauthorized actions.
Business users can notice exposed records or inappropriate permissions, but UAT is not a complete security assessment. Map applicable controls to specialist verification. The OWASP Application Security Verification Standard provides a structured basis for defining web-application security requirements and verification depth.
Keyboard use, focus order, labels, error identification, contrast, zoom, and assistive-technology compatibility affect whether people can complete work. Use the W3C Web Content Accessibility Guidelines 2.2 as the authoritative reference, then test the actual workflows, browsers, devices, and user needs in scope.
For mobile products, the mobile app testing checklist covers device, network, permission, store, performance, and release considerations. UAT should consume that technical evidence and focus business testing on whether users can complete the intended jobs under realistic operating conditions.
Triage each failed case by user impact, business impact, security or data risk, frequency, workaround, scope, and release consequence. Assign an owner and due date, document the decision, fix or accept explicitly, rerun the failed case, and perform regression around workflows the change could affect.
Severity describes impact; priority describes the order of response. A rare data-corruption defect may be severe even when few users encounter it. A visible wording issue may be urgent for launch communication but low severity. Define both scales before testing so schedule pressure does not rewrite risk after discovery.
A conditionally accepted defect should name the affected scenario, impact, workaround, owner, correction date, retest requirement, monitoring need, and approving authority. “Fix later” is not acceptance evidence. If a workaround depends on training, manual reconciliation, or support coverage, prove that control is available at launch.
Exit criteria should require planned critical scenarios to run, blockers to close, accepted exceptions to have owners, retests to pass, required specialist reviews to finish, and evidence to be complete. Sign-off must identify the build, scope, open risks, decision, conditions, approver, and effective date.
| Decision | Meaning | Required record |
|---|---|---|
| Go | Entry and exit criteria are met and remaining risk is accepted | Approved build, completed evidence, open-risk register, named signatory |
| Conditional go | Release may proceed only with explicit controls and deadlines | Conditions, workarounds, owners, dates, monitoring, and retest commitments |
| No-go | Release risk exceeds the approved threshold | Blocking failures, repair owner, next candidate build, and new test window |
Contractual acceptance and release readiness are related but not always identical. The software development RFP guide helps buyers request comparable acceptance, evidence, ownership, and support terms before selecting a vendor. The signed contract controls payment and remedies; operational UAT evidence informs the decision but is not legal advice.
A strong checklist prevents testing a moving build, using only happy paths, asking developers to approve themselves, copying unsafe production data, omitting integrations or roles, inventing pass rules after failures, treating screenshots as complete evidence, accepting vague defects, skipping retests, and signing without named authority.
These answers cover timing, ownership, templates, tester selection, failure handling, and the relationship between UAT and launch. The correct depth depends on business risk, system complexity, integrations, data sensitivity, user roles, contractual terms, and applicable obligations, so thresholds should be approved for the actual project.
Begin formal UAT after the candidate build is stable enough for end-to-end use, prerequisite system and integration testing has passed, environments and data are ready, and entry criteria are met. Plan UAT earlier, during requirements and contracting, so acceptance criteria and tester availability do not become late surprises.
The signatory should be the named business authority accountable for the outcome and authorized to accept remaining risk. Product owners or representative users may recommend approval, while security, finance, privacy, or compliance owners approve their domains. The vendor should not be the only party accepting its own work.
Yes, if the spreadsheet preserves identifiers, requirements, versions, roles, data, expected and actual results, evidence links, defects, retests, decisions, and access control. Larger or regulated projects may need a test-management system for audit trails, permissions, workflow, scale, and reliable linkage between results and changes.
Record the actual result and evidence, create a linked defect, assess impact and release consequence, assign ownership, then decide whether to fix, defer with explicit acceptance, or block release. After repair, rerun the failed case and relevant regression scenarios against the identified candidate build.
No. UAT provides evidence that agreed business scenarios work and that known residual risks were handled through an approved decision. It cannot prove every possible condition. Technical QA, security, performance, accessibility, monitoring, support, backup, rollback, and post-launch learning remain necessary controls.
Payment milestones should follow the signed contract, which may connect payment to deliverables, acceptance criteria, cure periods, and approval. Define that relationship before work begins. UAT evidence can support acceptance, conditional acceptance, or rejection, but businesses should obtain legal advice for contract language and remedies.
LeWebsite can turn requirements into traceable scenarios, prepare environments and data, coordinate representative testers, validate integrations and permissions, document defects and retests, define exit criteria, and package sign-off evidence. The goal is a controlled business decision about release, not a ceremonial checklist completed after development.
Use the website handover checklist when acceptance also involves source files, credentials, domains, analytics, documentation, and ownership transfer. To plan UAT for custom software, a portal, CRM workflow, or business application, contact LeWebsite with the scope, users, critical workflows, integrations, release window, and acceptance terms.
If this article raised questions about your own site, book 20 minutes with Francisco or send us a WhatsApp. No commitment, no long forms.
Or by phone: +1 (713) 396-5007 · +503 7931-1403
Subscribe to our
newsletter.
Get valuable strategy, culture, and brand insights straight to your inbox.
By signing up to receive emails from Motto, you agree to our Privacy Policy. We treat your info responsibly. Unsubscribe anytime.